> ## Documentation Index
> Fetch the complete documentation index at: https://launchdarkly.com/docs/llms.txt
> Use this file to discover all available pages before exploring further.

# My DEF CON 33 experience

export const BlogAuthor = ({date, avatar, alt, name}) => {
  return <div className="-mb-4">
      <p className="m-0 text-base font-semibold">
        <em>Published {date}</em>
      </p>
      <div className="flex items-center -mt-4">
        {avatar && <img src={avatar} alt={alt} className="h-8 w-8 rounded-full m-0" />}
        <p className="ml-[5px] text-lg">{name}</p>
      </div>
    </div>;
};

<View title="Developer" />

<View title="Federal docs" />

<View title="EU docs" />

<BlogAuthor date="September 11th, 2025" avatar="/images/authors/mike-rose.png" alt="Portrait of Mike Rose." name="by Mike Rose, Senior IT Security Engineer, LaunchDarkly" />

## 👋 Introduction

I attended [**DEF CON 33**](https://defcon.org/ "https://defcon.org/") this year in Las Vegas and want to share a recap of my experiences and insights from the event. Whether you’re a seasoned security practitioner or just DEF CON-curious, I hope this gives you a helpful window into what goes on at one of the world’s largest hacker conferences.

**Spoiler alert**: AI dominated the conference discussions.

***

## 🎯 Why I attended

I went into DEF CON this year with a few goals in mind:

1️⃣ Stay up-to-date on emerging threats.

2️⃣ Find practical inspiration for our security workflows at LaunchDarkly.

3️⃣ Catch up with old friends and colleagues.

***

## 🔍 Favorite talks & villages

### Talks

### 📍 Amplifying Phishing Attacks with Generative AI

* **Speaker**: Daniel Marques

* **What it was about**: This talk examined how AI allows threat actors to automate key phases of phishing campaigns, including initial reconnaissance, crafting targeted communications, and establishing attack infrastructure.

* **Why it stood out**: Threat actors can now easily scale and customize phishing campaigns using AI, which was previously more challenging with manual methods.

### 📍 Zero Trust, Total Bust - Breaking into thousands of cloud-based VPNs with one bug

* **Speaker**: David Cash & Rich Warren

* **What it was about**: This talk highlighted how Zero Trust Network Access (ZTNA) solutions were exploited to bypass authentication, spoof device posture checks, and escalate privileges.

* **Why it stood out**: This presentation aimed to highlight the vendor flaws of Zero Trust solutions. The key takeaway is to avoid blindly trusting your Zero Trust solution; consistently monitor logs and keep your infrastructure updated.

### Villages

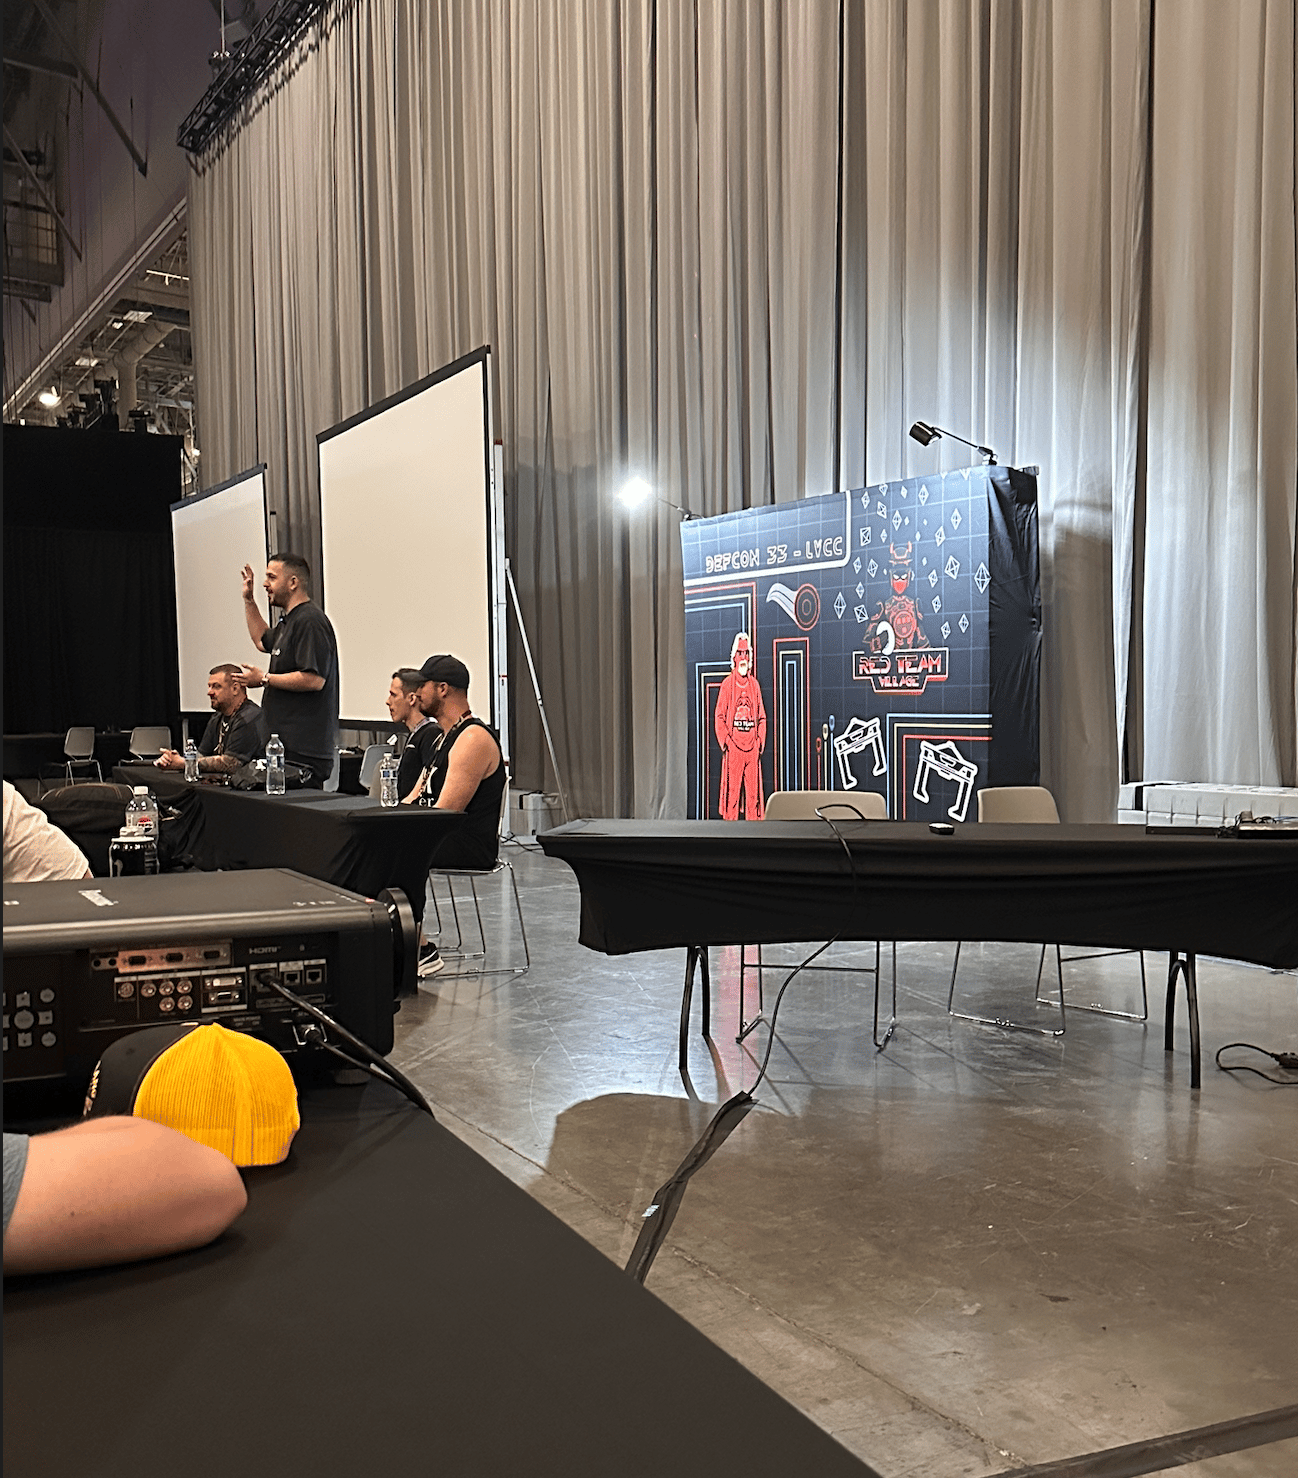
### 🧪 Red Team Village

* **What I explored**: Modern red team tools and methodologies for penetration testers and red team engagements.

* **Key insight**: I discovered some tools that I can leverage during our upcoming internal red team exercise for FedRAMP.

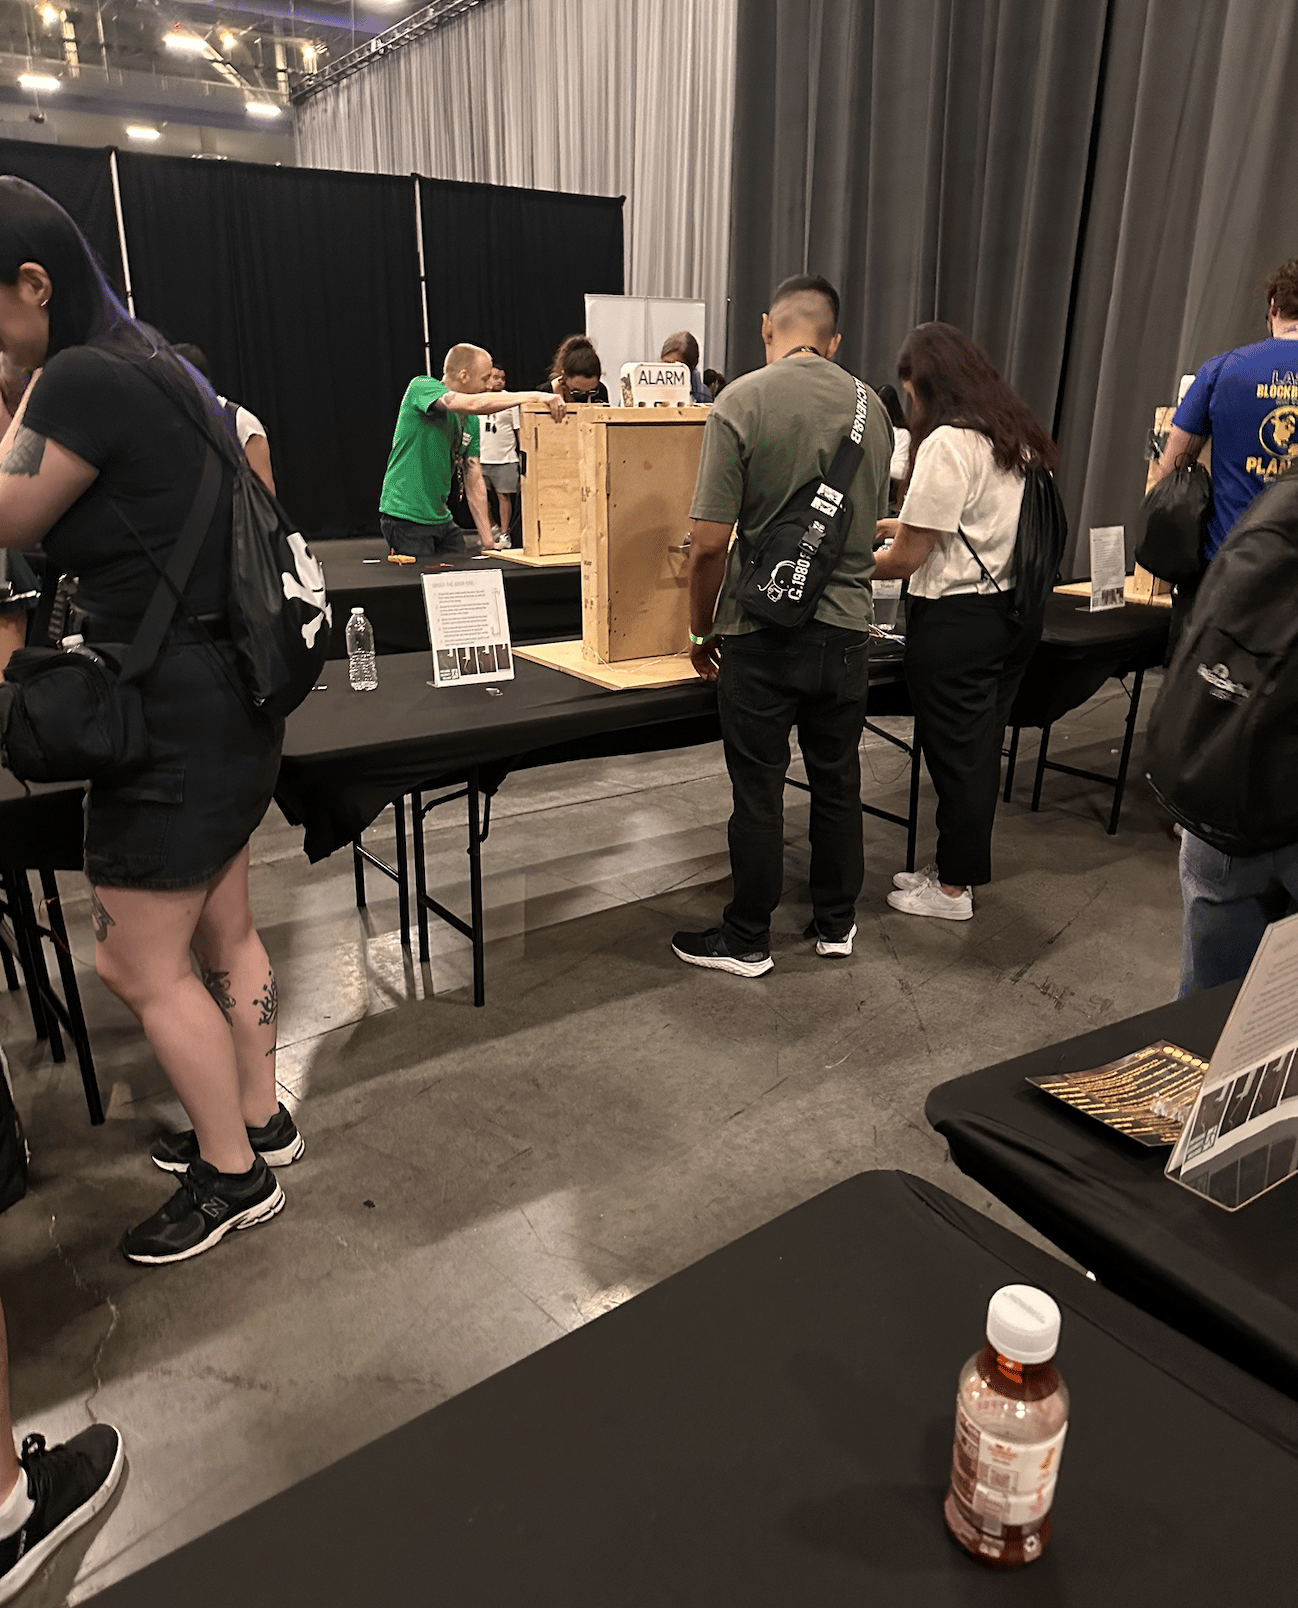
### 🧪 Physical Security Village

* **What I explored**: This year I volunteered for the Physical Security Village despite having limited experience with physical penetration testing.

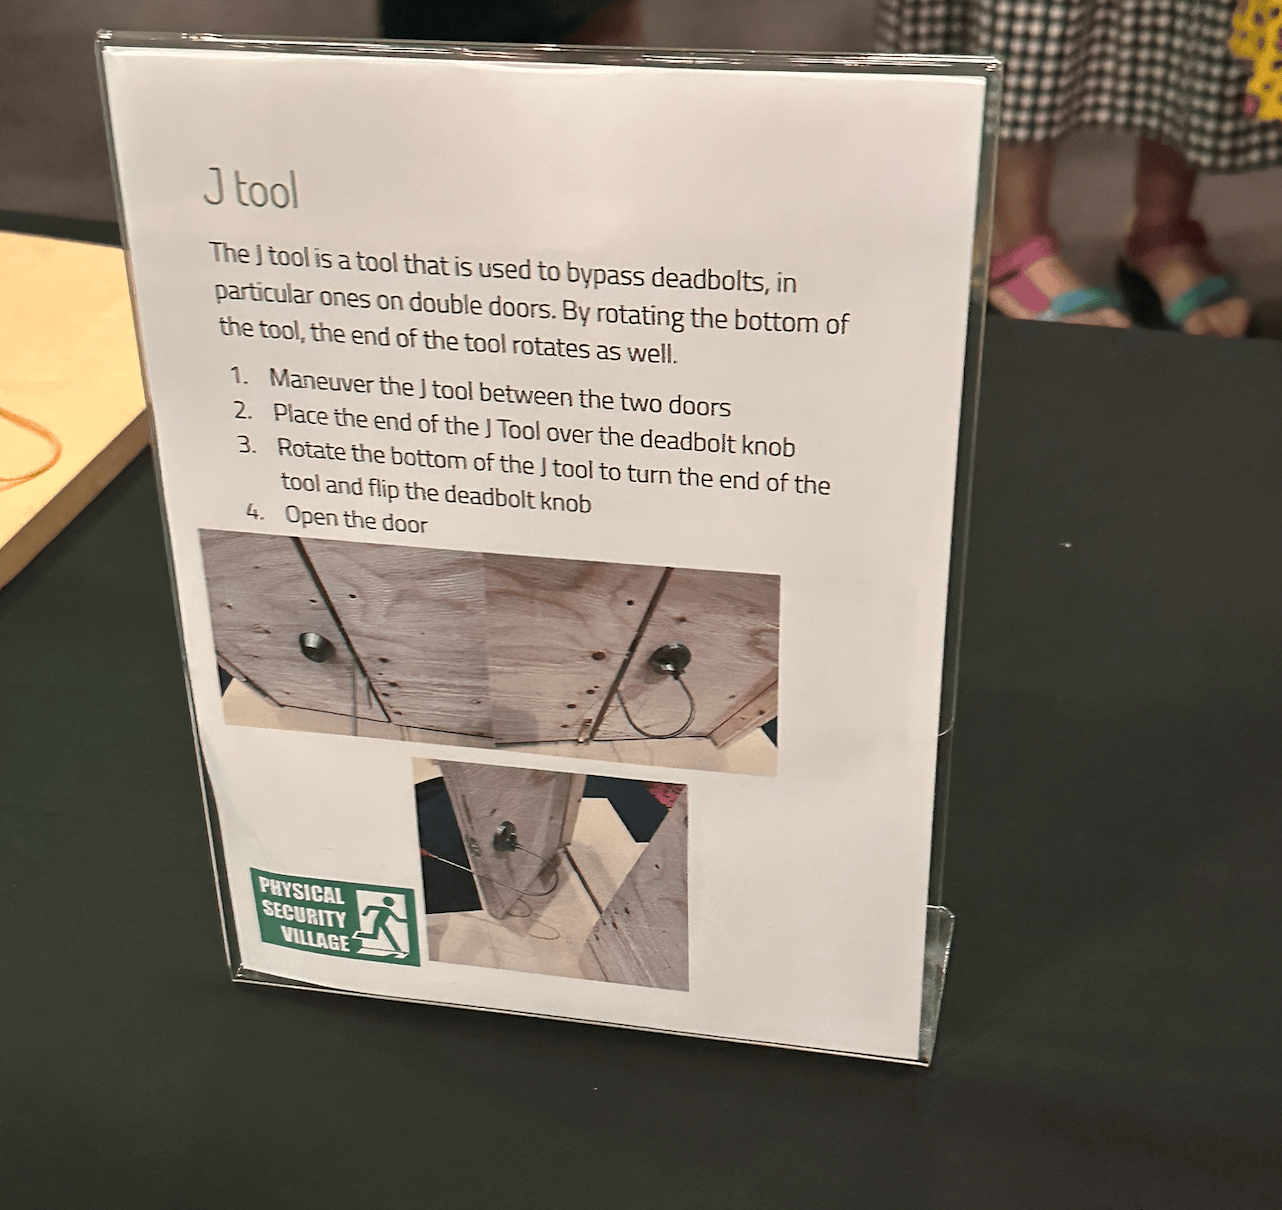
* **Key insight**: I learned various lock bypass techniques and demonstrated them to other conference attendees.
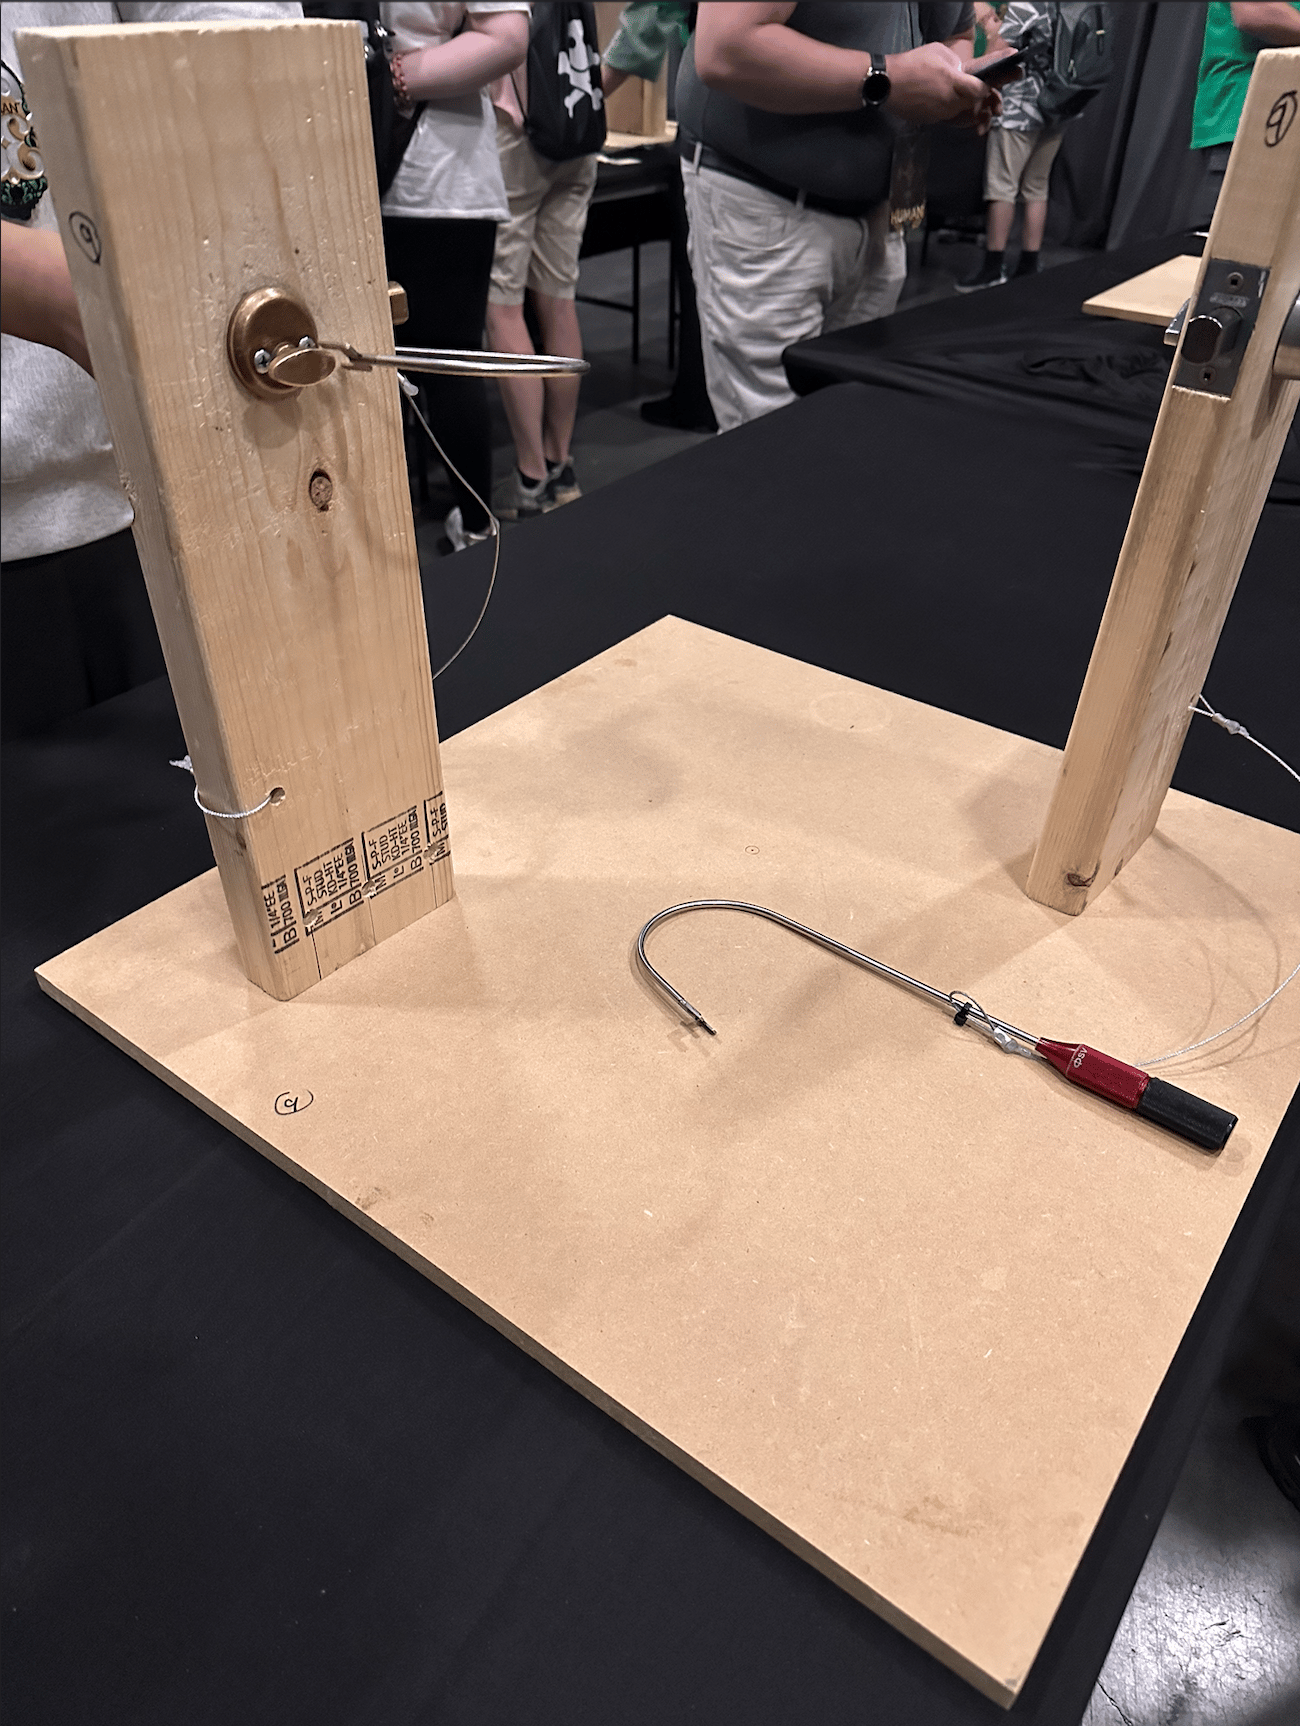
<Frame caption="Photo of a J-Tool demonstration..">
  <img src="https://mintcdn.com/launchdarkly/ppwc2LYsjE8wwIC_/images/blog/defcon-33-takeaways/j-tool-demonstration.png?fit=max&auto=format&n=ppwc2LYsjE8wwIC_&q=85&s=4a1f5da9bfd372adfe5dec2ae46f4633" alt="Photo of a J-Tool demonstration." width="1300" height="1726" data-path="images/blog/defcon-33-takeaways/j-tool-demonstration.png" />
</Frame>

***

## 🔒 Practical takeaways

Here are a few ideas or trends to dig into:

* **We should consider leveraging AI more to perform log analysis.**

* **Prompt injections will become more prevalent with LLM adoption.**

* **AI is enabling threat actors to launch hyper personalized, convincing, and adaptive phishing campaigns.**

***

## 👀 Noteworthy quotes

<Error>“Attackers have traditionally held the advantage in security, moving quickly and adapting swiftly. However, defenders using AI and automation are shifting this narrative.”</Error>

<Error>“We don’t have true artificial intelligence; we have a system skilled in pattern recognition that can provide relevant information.”</Error>

Sources for these quotes were smart folks at a happy hour I attended, but I didn’t catch their names.

***

## 📸 Photo dump
<Frame caption="Red Team Village panel">
  <img src="https://mintcdn.com/launchdarkly/ppwc2LYsjE8wwIC_/images/blog/defcon-33-takeaways/red-team-village-panel.png?fit=max&auto=format&n=ppwc2LYsjE8wwIC_&q=85&s=aaa1047dee9baa24c2d0cc68e9d00231" alt="Photo of Red Team Village panel." width="1298" height="1478" data-path="images/blog/defcon-33-takeaways/red-team-village-panel.png" />
</Frame>

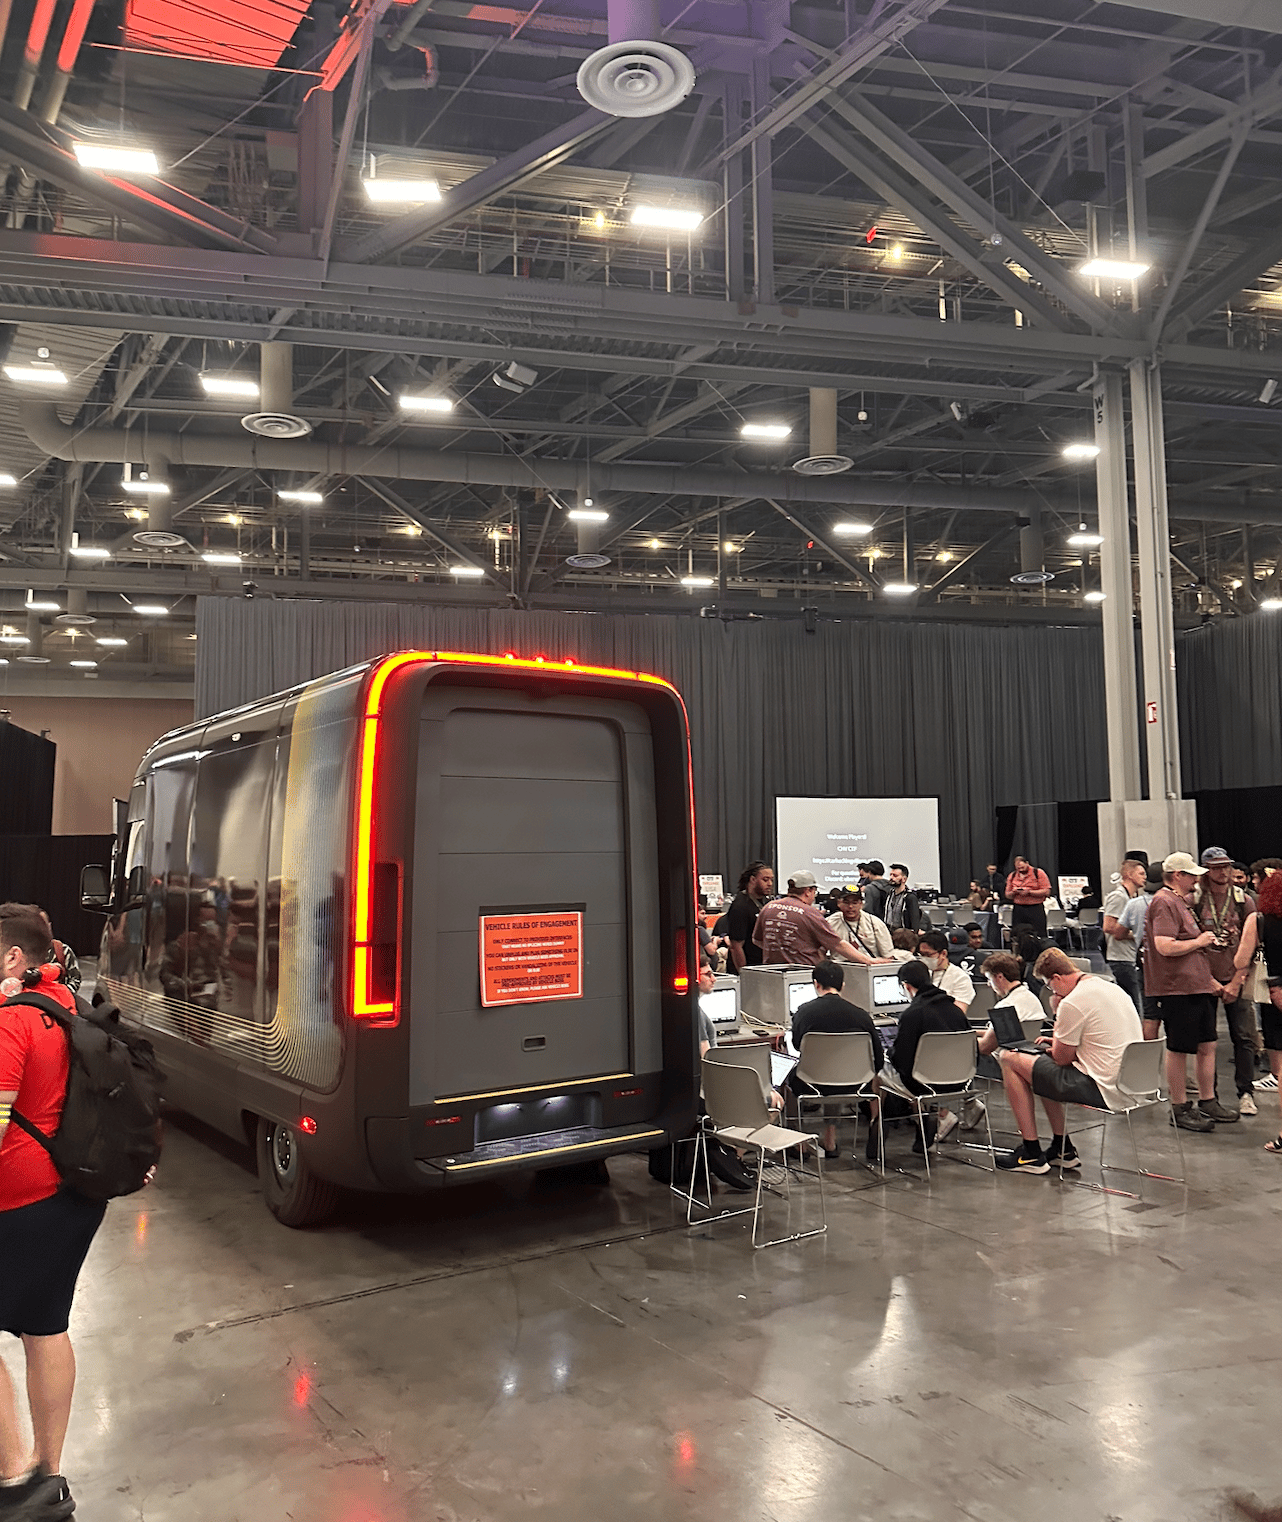
<Frame caption="Car hacking village">
  <img src="https://mintcdn.com/launchdarkly/ppwc2LYsjE8wwIC_/images/blog/defcon-33-takeaways/car-hacking-village.png?fit=max&auto=format&n=ppwc2LYsjE8wwIC_&q=85&s=e9ccaec652830cfbd35f029b259fde27" alt="Photo of car hacking village." width="1282" height="1522" data-path="images/blog/defcon-33-takeaways/car-hacking-village.png" />
</Frame>

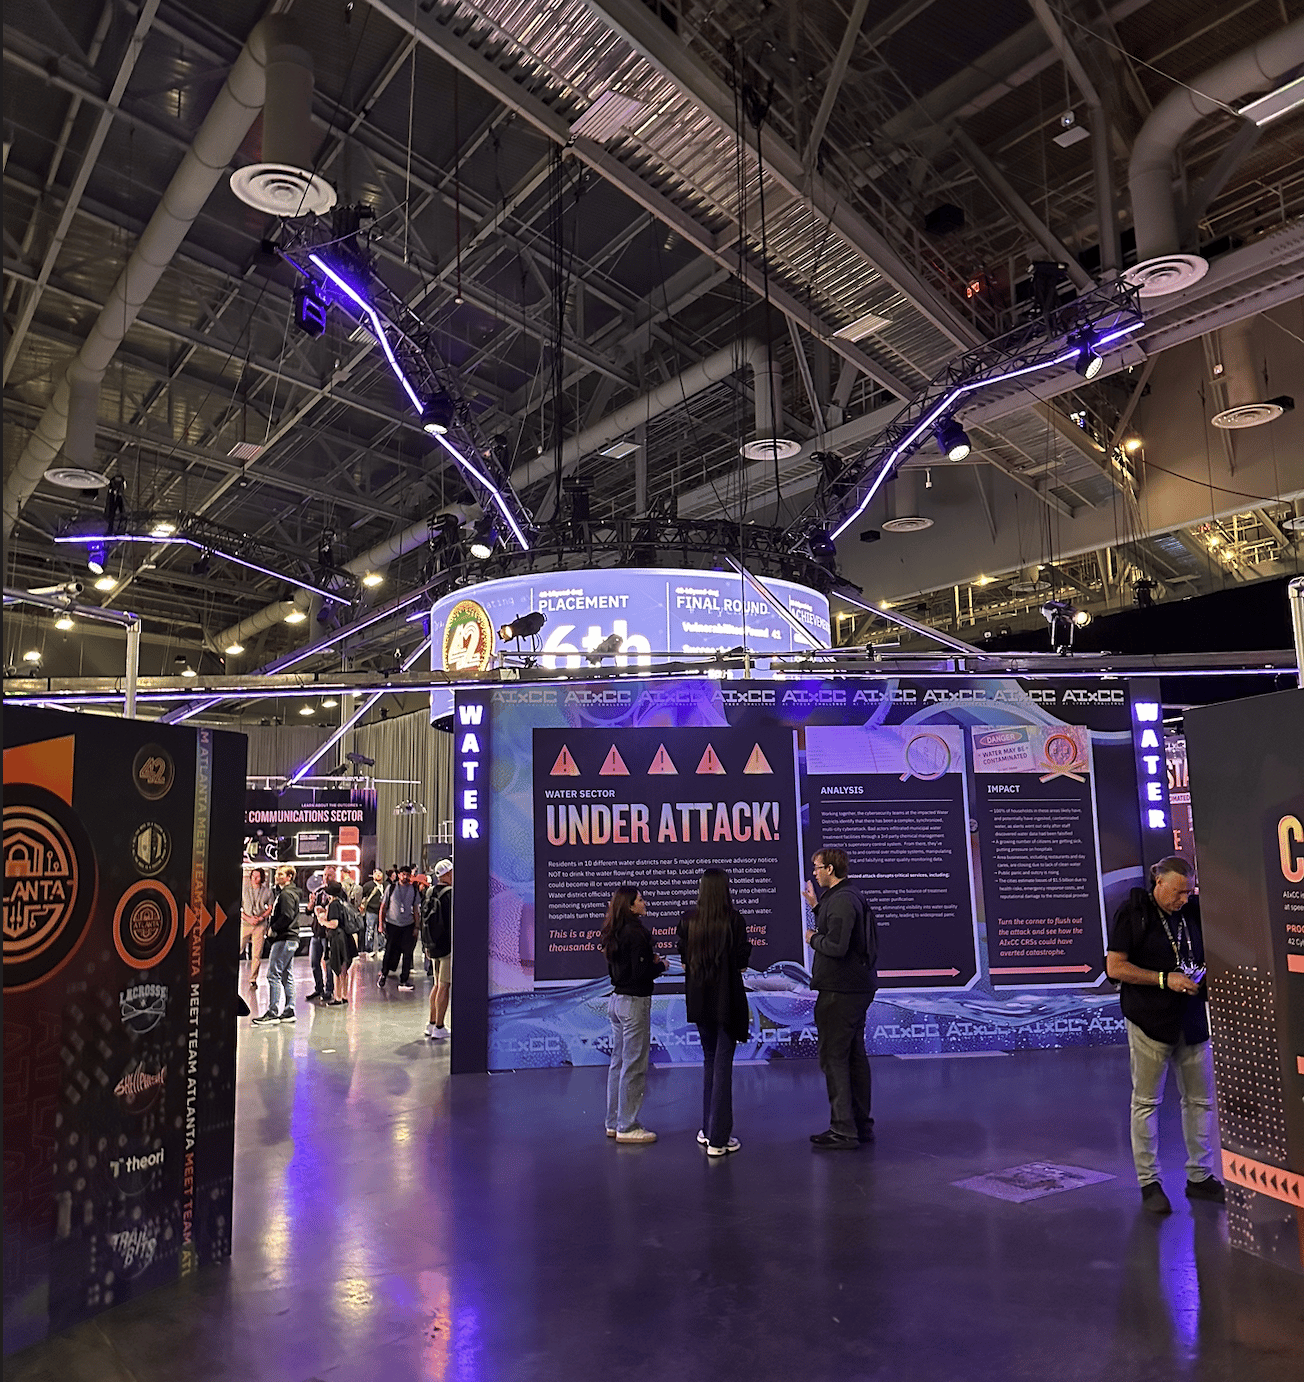
<Frame caption="AIXCC exhibit">
  <img src="https://mintcdn.com/launchdarkly/ppwc2LYsjE8wwIC_/images/blog/defcon-33-takeaways/aixcc-exhibit.png?fit=max&auto=format&n=ppwc2LYsjE8wwIC_&q=85&s=2a39f37a4171830c5c10af56b21e7b49" alt="Photo of AIXCC exhibit." width="1304" height="1382" data-path="images/blog/defcon-33-takeaways/aixcc-exhibit.png" />
</Frame>

<Frame caption="Physical Security Village">
  <img src="https://mintcdn.com/launchdarkly/ppwc2LYsjE8wwIC_/images/blog/defcon-33-takeaways/physical-security-village.png?fit=max&auto=format&n=ppwc2LYsjE8wwIC_&q=85&s=f882765f61dfc1a8261e1ca6ce1c8953" alt="Photo of Physical Security Village." width="1298" height="1608" data-path="images/blog/defcon-33-takeaways/physical-security-village.png" />
</Frame>

<Frame caption="J-Tool instructions">
  <img src="https://mintcdn.com/launchdarkly/ppwc2LYsjE8wwIC_/images/blog/defcon-33-takeaways/j-tool-instructions.png?fit=max&auto=format&n=ppwc2LYsjE8wwIC_&q=85&s=4992a8d9037356f4756a55e3f55a2411" alt="Photo of J-Tool instructions." width="1282" height="1210" data-path="images/blog/defcon-33-takeaways/j-tool-instructions.png" />
</Frame>

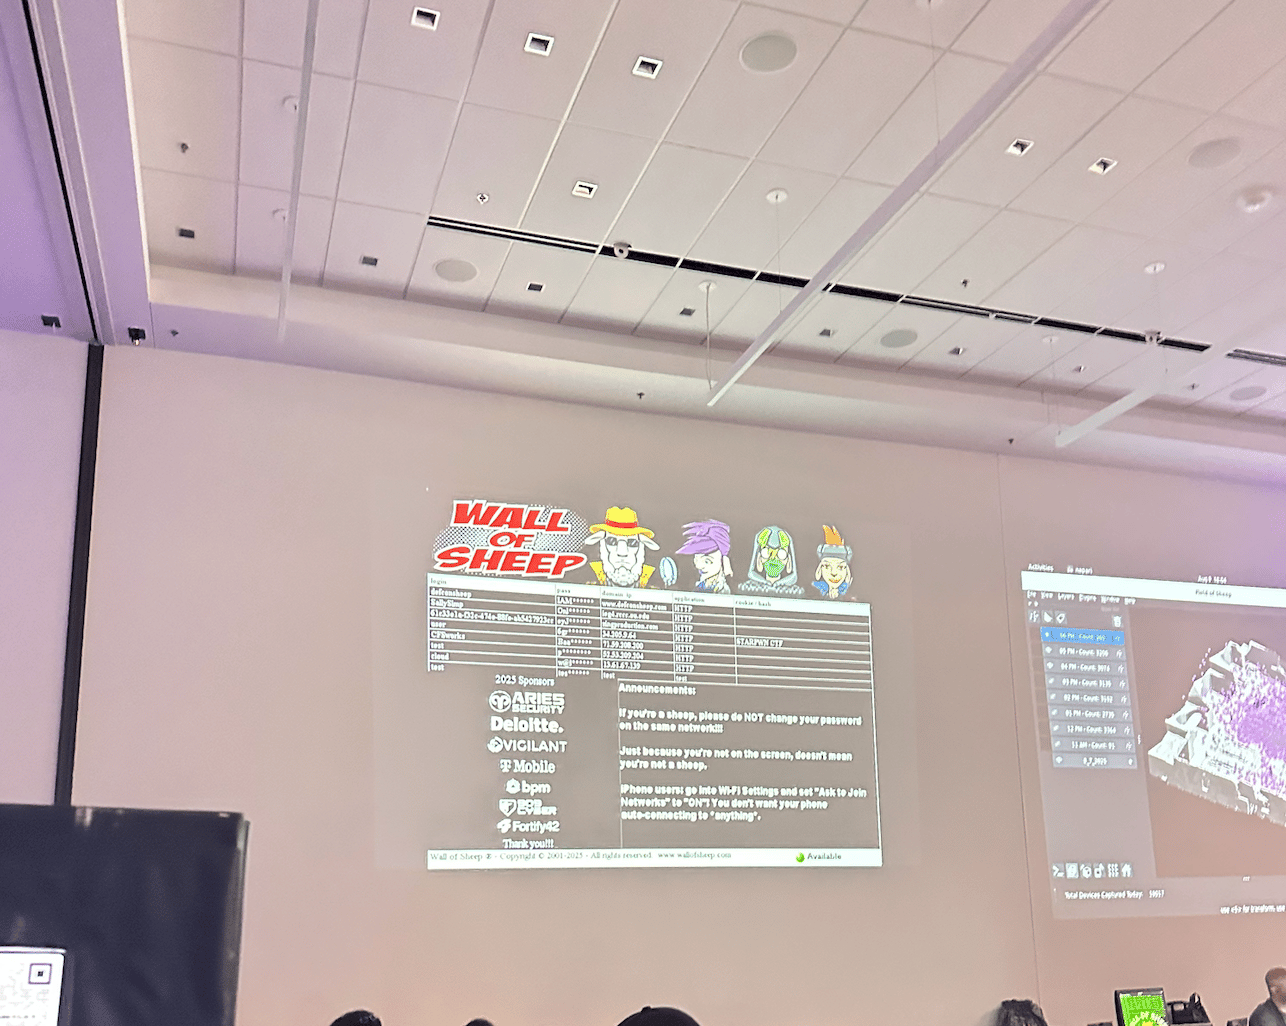
<Frame caption="Wall of sheep">
  <img src="https://mintcdn.com/launchdarkly/ppwc2LYsjE8wwIC_/images/blog/defcon-33-takeaways/wall-of-sheep.png?fit=max&auto=format&n=ppwc2LYsjE8wwIC_&q=85&s=af2af7bff0cf80c76ea9d2ae2e025e1f" alt="Photo of wall of sheep who have been pwned at defcon 33." width="1286" height="1026" data-path="images/blog/defcon-33-takeaways/wall-of-sheep.png" />
</Frame>

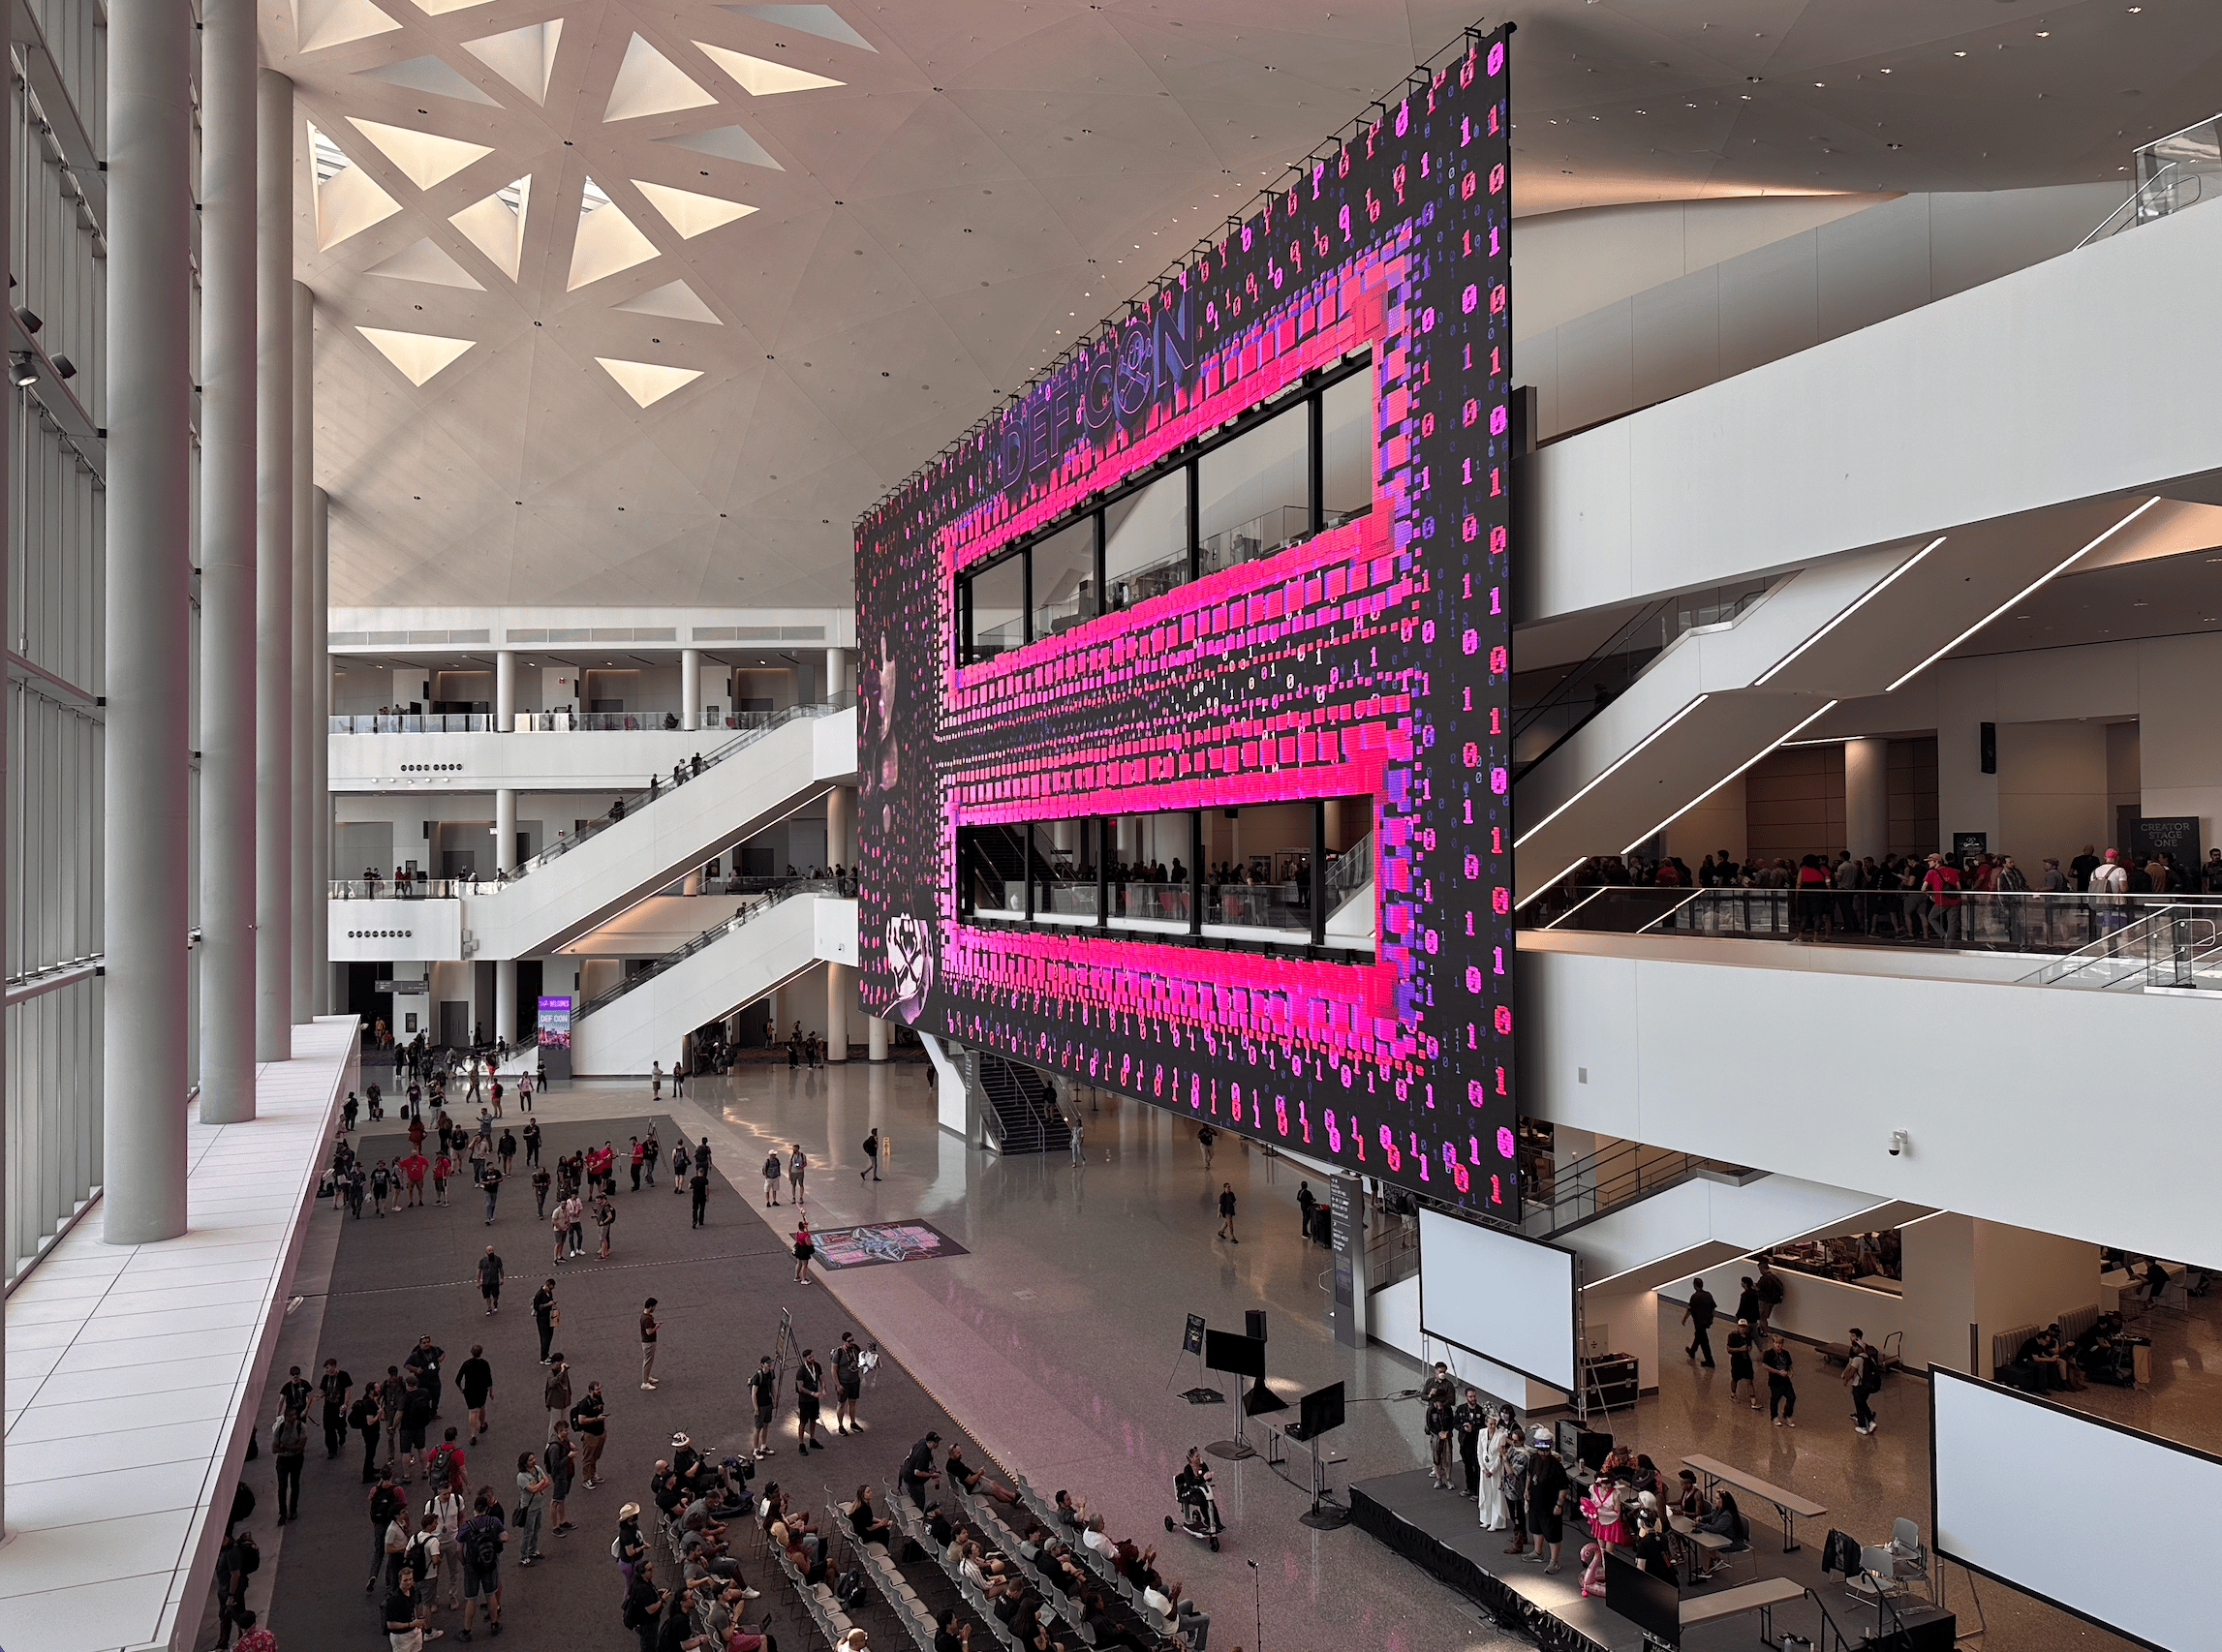
<Frame caption="Inside lvcc">
  <img src="https://mintcdn.com/launchdarkly/ppwc2LYsjE8wwIC_/images/blog/defcon-33-takeaways/inside-lvcc.png?fit=max&auto=format&n=ppwc2LYsjE8wwIC_&q=85&s=14e641e226903f1bb7f98354cd2991f1" alt="Photo of the inside of lvcc." width="2294" height="1706" data-path="images/blog/defcon-33-takeaways/inside-lvcc.png" />
</Frame>

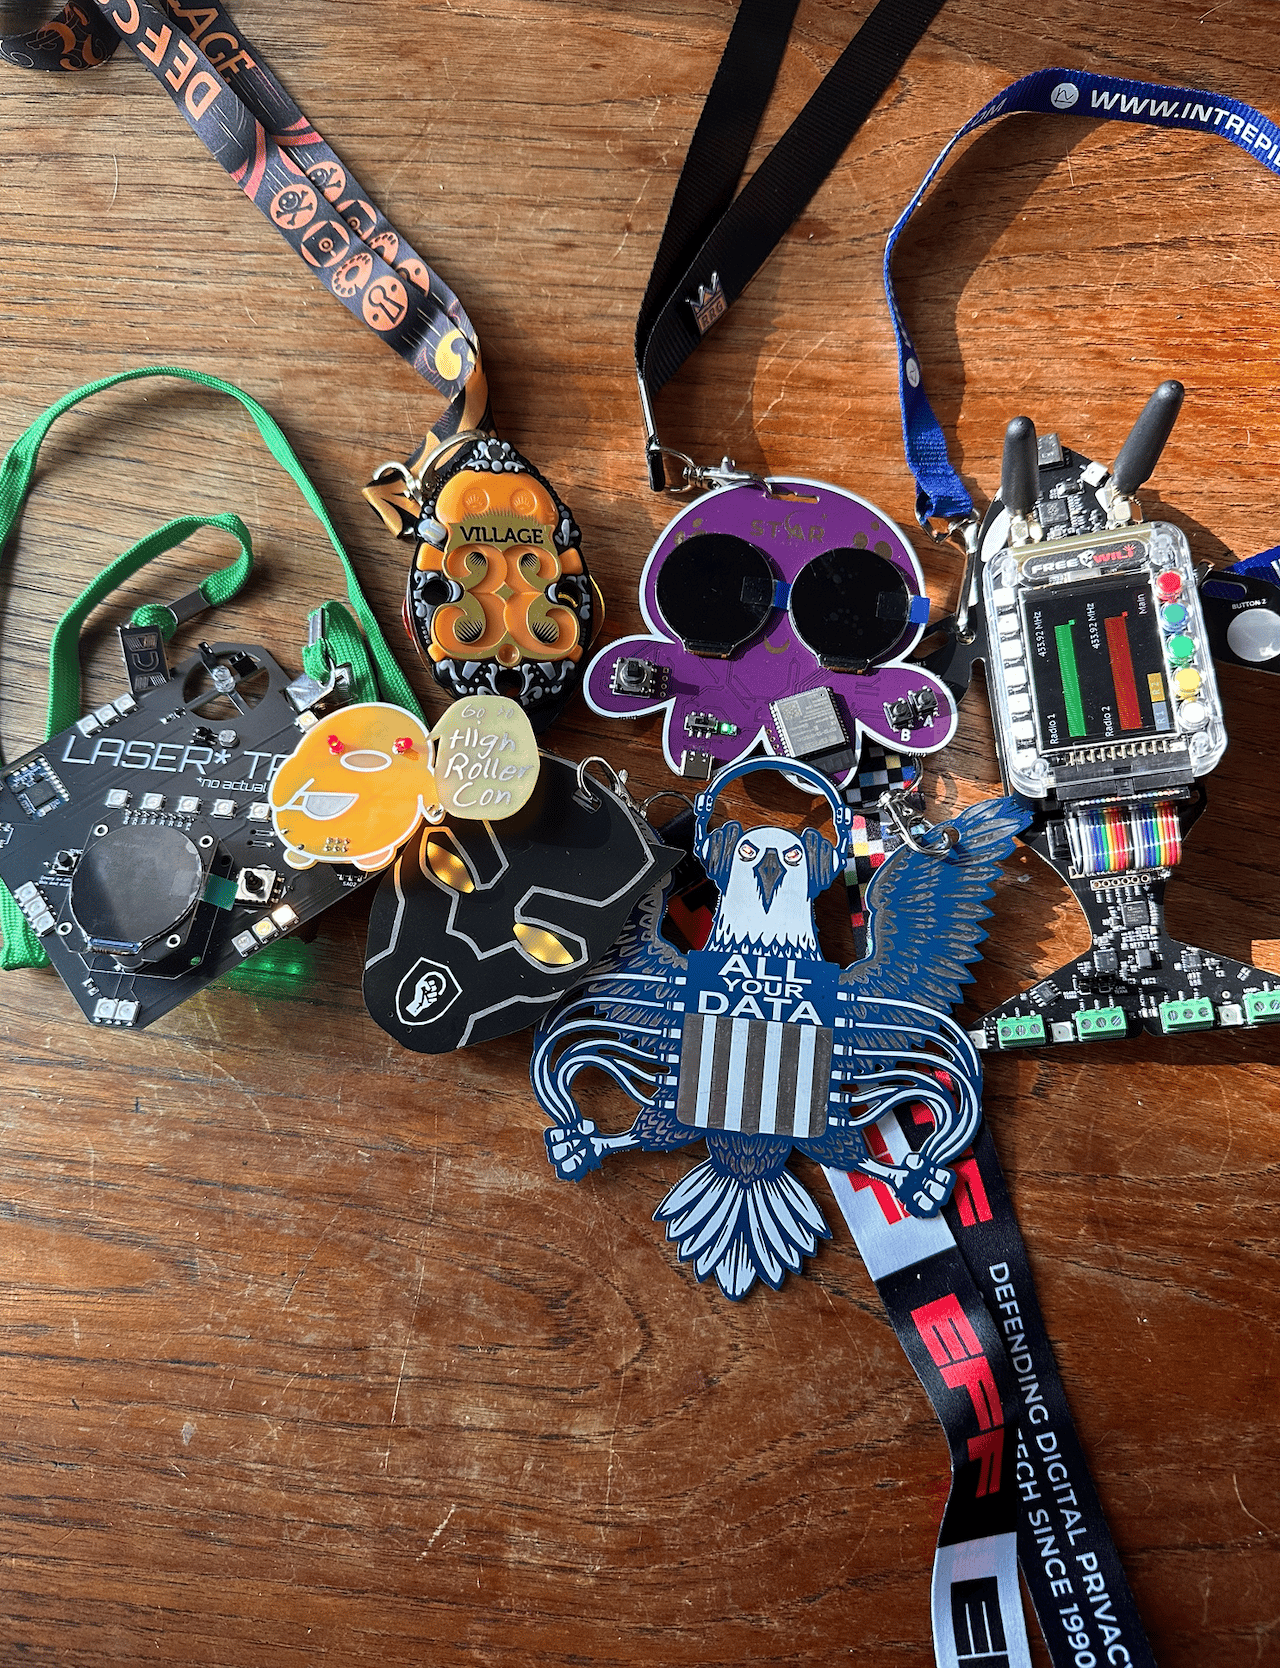
<Frame caption="I am running out of space for the badges I collect each year at DEF CON. 😆">
  <img src="https://mintcdn.com/launchdarkly/ppwc2LYsjE8wwIC_/images/blog/defcon-33-takeaways/badge-collection.png?fit=max&auto=format&n=ppwc2LYsjE8wwIC_&q=85&s=8d9431e6f22b0847e88a30b689341896" alt="A cool collection of six previous defcon badges." width="1280" height="1668" data-path="images/blog/defcon-33-takeaways/badge-collection.png" />
</Frame>

My favorite badge this year was the [Laser Tag Badge](https://www.dani.pink/lasertag/about "https://www.dani.pink/lasertag/about"). Unfortunately, my IR emitter fell off on the first day of the Con. I soldered on a new one but finished 160th on the leaderboard.

## 💭 Final thoughts

This was my fourth DEF CON and it’s always a bit overwhelming—in the best way. It’s a reminder of the creativity, curiosity, and persistence that defines the security community. Whether you’re trying to break things or protect them, it’s all about asking better questions.